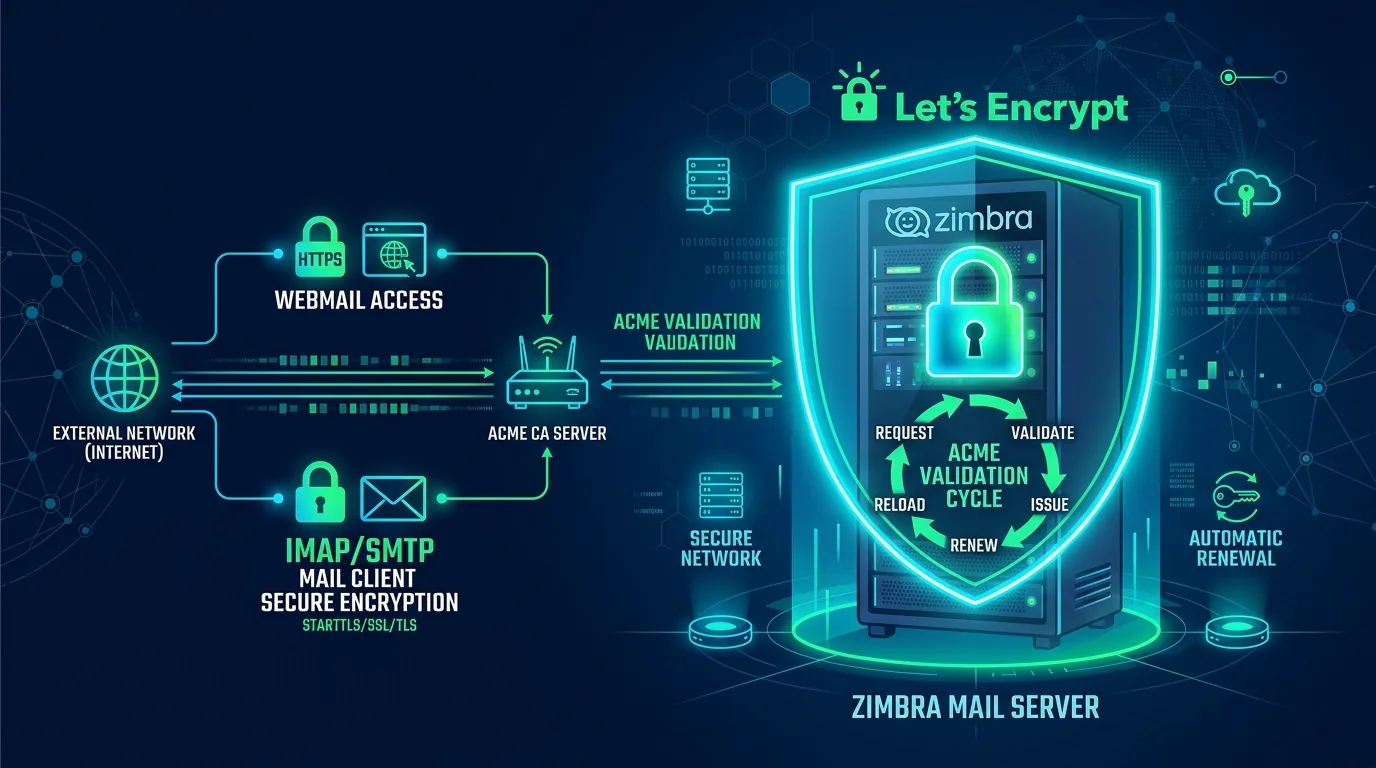
This guide explains how to obtain and deploy Let’s Encrypt certificates on ZCS 8.8, 9.0, and 10.0 using Certbot and the ISRG Root X2 chain.
- Verify
zmhostnamematcheshostname --fqdn, check CAA DNS records forletsencrypt.org, and ensure port 80 is free (switch Zimbra Proxy to HTTPS-only if needed). - Install Certbot in
/opt/certbot/and request the certificate with--standalone --preferred-chain "ISRG Root X2". - Append
isrg-root-x2.pemtochain.pem, copyprivkey.pemtocommercial.key, deploy withzmcertmgr deploycrt comm, and restart Zimbra viazmcontrol restart.
Need Expert Support for Your Zimbra Server?
Contact our team for setup, migration, SSL/TLS, performance tuning, and 24/7 SLA maintenance.